Tested by hand
Scanners find the obvious. Access-control gaps, tenant isolation failures and business-logic abuse need someone who understands what the application is for.
web application & api penetration testing
Manual testing of your web application and the APIs behind it, for SaaS, health-tech and medical-device software. Fixed price agreed before we start, a report your developers can act on, and a free retest when you have fixed things.
Fixed-price quote within 2 working days of the scoping call.
# severity summary — example output, not a real client
CRITICAL  1  Broken access control: role B reads role A records
HIGH      2  Tenant isolation bypass via object identifier
HIGH         Session not invalidated after password change
MEDIUM    4  ...
LOW       6  ...

→ each finding: evidence, reproduction steps, CVSS, fix guidance
→ retest of fixed findings included
what you get
Scanners find the obvious. Access-control gaps, tenant isolation failures and business-logic abuse need someone who understands what the application is for.
Every finding has evidence, reproduction steps, a CVSS rating and fix guidance written for the developer who has to make the change.
Fix the findings and we verify them, then issue a retest letter you can show customers and auditors.
You know who is testing your application, and you talk to that person directly. No hand-off to a junior after the sales call.
services
Every engagement is scoped on a short call and priced before it starts. If a smaller scope would answer your question, we will say so.
Manual testing of your web application and the APIs behind it, authenticated as every user role, against the OWASP testing guides.
From £2,950per application, fixed price after scoping
See what's included →The same testing, plus the evidence structure that regulatory submissions and notified-body reviews ask for.
From £5,950per application, fixed price after scoping
See what's included →A configuration and identity review of the Azure environment your application runs in, with prioritised, practical fixes.
From £1,950per environment, fixed price after scoping
See what's included →how it runs
You always know what is happening, what has been found so far, and what happens next. Critical findings are reported the moment they are confirmed.
A short call about the application, its roles and what would hurt most if it broke. You get a fixed-price proposal and dates.
Rules of engagement, authorisation and an NDA if you want one. Testing starts only once these are signed.
Reconnaissance and mapping: every route, role, parameter and API call that makes up the attack surface.
Manual testing against the OWASP guides, supported by tooling. Critical findings are reported the moment they are confirmed, not held for the report.
SaaS            customer security reviews, ISO 27001 evidence,
                a new release or authentication model

Health-tech     portals handling patient or clinical data,
                NHS and hospital security questionnaires

Medical device  SaMD and connected-device web interfaces
                needing evidence for FDA or EU MDR files

Scale-ups       growing fast, no in-house security engineer
who it's for
Testing a web application well means understanding what it is supposed to do, and who is supposed to be able to do it. That is harder, and more valuable, when the application carries clinical or personal data and someone will eventually audit it.
The medical-device package exists because device makers need more than a findings list: they need test evidence structured for a submission or a technical file.
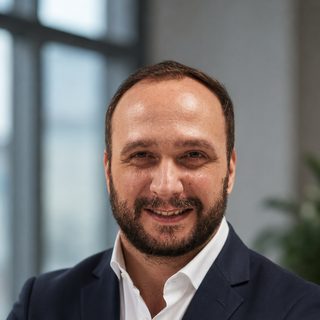
who tests it
I'm Alex Adamovici. I've spent my career in security engineering across regulated industries: cloud architecture, identity and access management, and the security evidence that regulated products have to produce. I test the applications I'm engaged for personally, and I write the report myself.
request a scope
A 20-minute scoping call, then a fixed-price proposal. No obligation, and no pressure to buy a bigger scope than you need.
Fixed-price quote within 2 working days of the scoping call · Report delivered within 5 working days of testing ending · One retest of fixed findings included, within 60 days