I test it myself
The person on the scoping call is the person testing your application and writing your report. Nothing is handed to a junior after you sign.
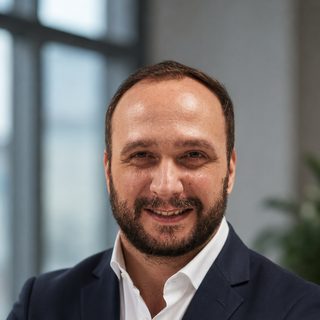
who tests your application
I've spent my career in security engineering in regulated environments: cloud architecture, identity and access management, and the security evidence that regulated products have to produce. Web application testing is where those threads meet, and it is what this service does.
My work sits where security engineering meets regulated software. I have designed and implemented security and access controls on cloud platforms, run identity and access management for systems that auditors look at closely, and worked on the security documentation that medical-device and health-software companies have to produce for regulators and customers.
That mix is the reason this service exists. Plenty of testers can find a vulnerability. Fewer can explain it in a way that satisfies an auditor, a notified body reviewer or a hospital's security team, and fewer still can tell you which findings genuinely matter for the product you are building.
Penetration testing is a different purchase from compliance consultancy, with different buyers and a different rhythm. It sits on its own here so the scope, the price and the boundaries are unambiguous. The engagement is contracted and invoiced by MD QMS Ltd., and testing work stays independent of any consultancy that company does for you.
St Helens, Merseyside. Testing is remote; scoping and debrief calls can be on-site in the UK if you prefer.
This service is delivered by me and contracted through MD QMS Ltd., a UK compliance and technology consultancy. If you also need the wider security or regulatory documentation built, that is what the main practice does.
mdqms.co.uk →how i work
The person on the scoping call is the person testing your application and writing your report. Nothing is handed to a junior after you sign.
I take on a limited number of tests at a time so each one gets proper attention, and so dates I give you hold.
If a finding is theoretical, I will say so. Inflating severity to make a report look impressive wastes your engineers' time.
Reports are written knowing they will be read by customers, auditors and sometimes regulators, so the evidence holds up when it is forwarded.
request a scope
A 20-minute scoping call, then a fixed-price proposal. No obligation, and no pressure to buy a bigger scope than you need.
Fixed-price quote within 2 working days of the scoping call · Report delivered within 5 working days of testing ending · One retest of fixed findings included, within 60 days